
Security
Frontier AI Models Significantly Accelerate the Discovery of Security Vulnerabilities
Palo Alto Networks Chief Product and Technology Officer Lee Klarich revealed in a blog post that the company, as a launch partner for Anthropic's Project Glasswing, tested frontier AI models such as Claude Mythos starting April 7, resulting in the disclosure of 26 CVEs in the first Patch Wednesday security advisory, far exceeding the usual 5. Klarich emphasized that merely running the models does not automatically solve problems; it requires building an AI scanning framework and adopting a multimodal approach. Meanwhile, Google and Microsoft also reported breakthrough progress in AI-driven vulnerability discovery.
Identity Security Rises as the Leading Cause of Enterprise Cyberattacks
According to Sophos's 2026 State of Identity Security report released on Tuesday, 70% of enterprises experienced at least one identity-related breach over the past year, with an average of three such incidents per company. Two-thirds of ransomware victims originated from identity issues, with an average recovery cost of $1.64 million. Based on a survey of 5,000 IT and cybersecurity leaders across 17 countries, the report indicates that identity has become the 'new perimeter' of cybersecurity, yet most enterprises still show significant gaps in monitoring and credential management.
Google Threat Intelligence: AI Can Now Generate Usable Zero-Day Vulnerabilities, First Empirical Evidence
Google Threat Intelligence Group (GTIG) released a report on Monday disclosing that a threat actor used AI to develop a usable zero-day vulnerability, believed to be the first successful case. The attack attempted to launch a large-scale exploitation event but was detected and prevented by Google in advance. GTIG has notified relevant developers and released a patch. The report also noted that hacker groups linked to North Korea and China have shown strong interest in AI-assisted vulnerability discovery.
Report: Enterprises Conceal the Vast Majority of Ransomware Attacks
A report released by security firm BlackFog on Wednesday indicated that the vast majority of global ransomware attacks in the first quarter of 2026 were not disclosed. Data shows that undisclosed attacks reached 2,160, nearly 10 times the 264 disclosed attacks. The United States was the main target, with manufacturing and healthcare being the most frequently attacked industries in undisclosed and disclosed attacks, respectively. The report also highlighted emerging attack tools and new risks brought by shadow AI.
Enterprises eagerly anticipate AI reshaping security strategies, but are underprepared
According to the Workforce Password Security Status Report released by Zoho on Tuesday, enterprises have high confidence in AI's ability to improve cybersecurity, but actual deployment readiness is severely lacking. The report indicates that 90% of respondents believe AI can strengthen network defenses, yet only 8% say they are currently prepared to deploy AI-driven security tools. Meanwhile, a large number of enterprises still show significant shortcomings in foundational security practices such as identity management and zero-trust networks.
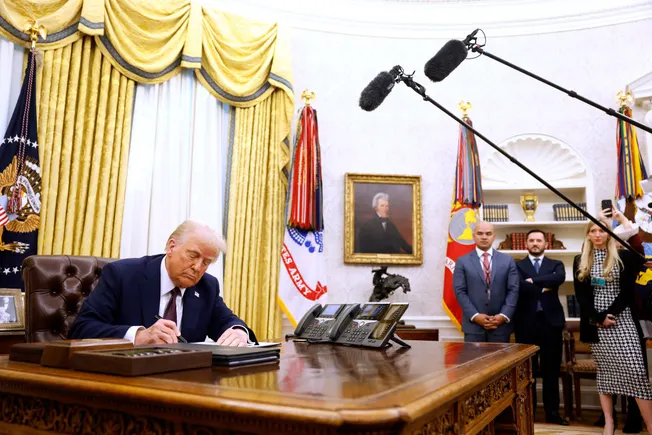
Google, Microsoft, and xAI Frontier AI Models to Undergo US National Security Testing
The AI Standards and Innovation Center (CAISI) under the US National Institute of Standards and Technology (NIST) announced agreements with Google DeepMind, Microsoft, and xAI to conduct safety assessments on their frontier AI models before public release and to provide continuous monitoring after deployment. This move expands on previous collaborations with OpenAI and Anthropic, aiming to address national security risks posed by AI. Analysts note that this marks a consideration of "sovereign alignment" factors when enterprises procure AI.
Agentic Browsers Reshape Enterprise Security Rules
With the rapid adoption of agentic AI, 74% of organizations plan to deploy it within two years (Deloitte), and 84% of knowledge workers expect its adoption (EY). Agentic browsers transform from passive tools into active agents, but security research has already identified multiple vulnerabilities. Risks include prompt injection hijacking, data leakage, accountability gaps, business risks, and shadow AI. Enterprises should achieve security governance through enterprise browsers with built-in DLP, identity, and runtime security (such as Prisma Browser), rather than simply banning them.
Mitigating Chain-of-Custody Risks: Why CIOs Are Bringing Data Destruction In-House
Data security does not end with device retirement; rather, risks escalate at the end of the lifecycle. Under strict scrutiny from frameworks such as NIST 800-88 and HIPAA, multiple handoffs in third-party destruction models are becoming a liability. This article analyzes why CIOs are bringing data destruction in-house and how this shift turns compliance pressure into a governance advantage.
Six Countries Including the US and Australia Jointly Release Guidelines for Safe Deployment of Agentic AI
Governments of six countries, including Australia and the United States, jointly released guidelines for the safe deployment of agentic AI, emphasizing prudent adoption, risk management, and human oversight.
Microsoft says Copilot growth strong, spending increases as revenue climbs
In its fiscal 2026 third-quarter earnings report, Microsoft disclosed that its AI business annualized revenue grew 123% year-over-year to over $37 billion, with Microsoft 365 Copilot paid seats exceeding 20 million. The company plans capital expenditures of over $40 billion next quarter and updated its partnership terms with OpenAI, while OpenAI announced it would bring its models to AWS. Analysts advise CIOs to choose cloud vendors flexibly based on specific use cases.